• Now booking Q3 · Montréal · Toronto · Miami · Rabat · • Odoo 17 migrations scheduling 6 weeks out

● ISO 27001:2022 cohort opening — Q3 2026 · 3 enrollments remaining

● Cybersecurity · GRC · ISO 27001 · Risk

Security that passes audit
and survives reality

A pragmatic ISO 27001 and GRC practice for Canadian and North-African SMBs. We scope your ISMS, write the policies your team will actually follow, and walk you through certification without the theatre.

Typically reply in 1 business day

ISMS · Meridian Bank · TorontoStage 2 certified
Gap assessmentW1–2 · CLOSED
Risk register · 47 risksW3 · APPROVED
Statement of ApplicabilityW5 · v1.2
93 Annex A controlsW6–22 · LIVE
Internal auditW26 · 3 NC · closed
Stage 1 & 2 auditW30–34 · PASS
Surveillance · Year 1Q2 2026 · PREP
What we deliver

Six programs, one methodology — scoped to your risk, not a template.

We don’t sell platforms. We write the documentation, run the workshops, build the evidence, and sit beside your team in the audit room.

01 · Assessment

Gap & maturity assessment

A structured, four-week review against ISO 27001:2022 and your sector’s baseline. Findings, remediation plan, and effort estimate.

  • Interviews & evidence walk
  • Control-by-control scoring
  • Prioritized 12-month plan
02 · ISMS

ISO 27001 implementation

End-to-end program: scope, risk methodology, SoA, Annex A controls, internal audit, and management review — through Stage 2 certification.

  • Scope statement & context
  • Risk register & treatment plan
  • Certification shepherding
03 · GRC

GRC program build

Policy library, control matrix, and evidence workflows in your GRC tool of choice — Vanta, Drata, or a properly-configured Odoo.

  • 22 core policies · EN/FR
  • Control-to-evidence mapping
  • Tool selection & setup
04 · Risk

Enterprise risk management

A risk register your board will read. Quantitative where we can (FAIR), qualitative where we must, reviewed on a quarterly cadence.

  • Risk taxonomy · tolerance
  • Quarterly risk committee
  • Third-party & vendor risk
05 · vCISO

Fractional CISO

A senior security leader on your exec team for 4–10 days a month. Strategy, board reporting, incident response, and vendor reviews.

  • Board & exec reporting
  • Incident-response lead
  • Audit & questionnaire owner
06 · Awareness

Security awareness & training

Programs your team completes on purpose — scenario-driven, bilingual, reinforced with phishing exercises that match your threat model.

  • All-staff curriculum · EN/FR
  • Role-based modules · dev / finance
  • Phishing cadence & reporting
ISO 27001:2022 · the path

From gap assessment to certificate, in twelve months.

A predictable cadence. Each phase has a written deliverable, a signed-off exit criterion, and a clear owner on your side. No surprises at the audit.

01
Month 1

Gap & scope

ISMS scope statement, stakeholder map, context of the organization, interested parties.

02
Month 2

Risk register

Risk methodology, asset inventory, threat library, scored register with treatment plan.

03
Month 3

SoA & policy

Statement of Applicability, 22 core policies, standards and procedures — all signed off.

04
Months 4–8

Control rollout

93 Annex A controls implemented with owners, cadence, and evidence workflows. You are here.

05
Months 9–10

Internal audit

Independent internal audit, nonconformity register, management review, corrective action.

06
Months 11–12

Certification

Stage 1 readiness audit, Stage 2 certification audit, closing NCs, certificate issued.

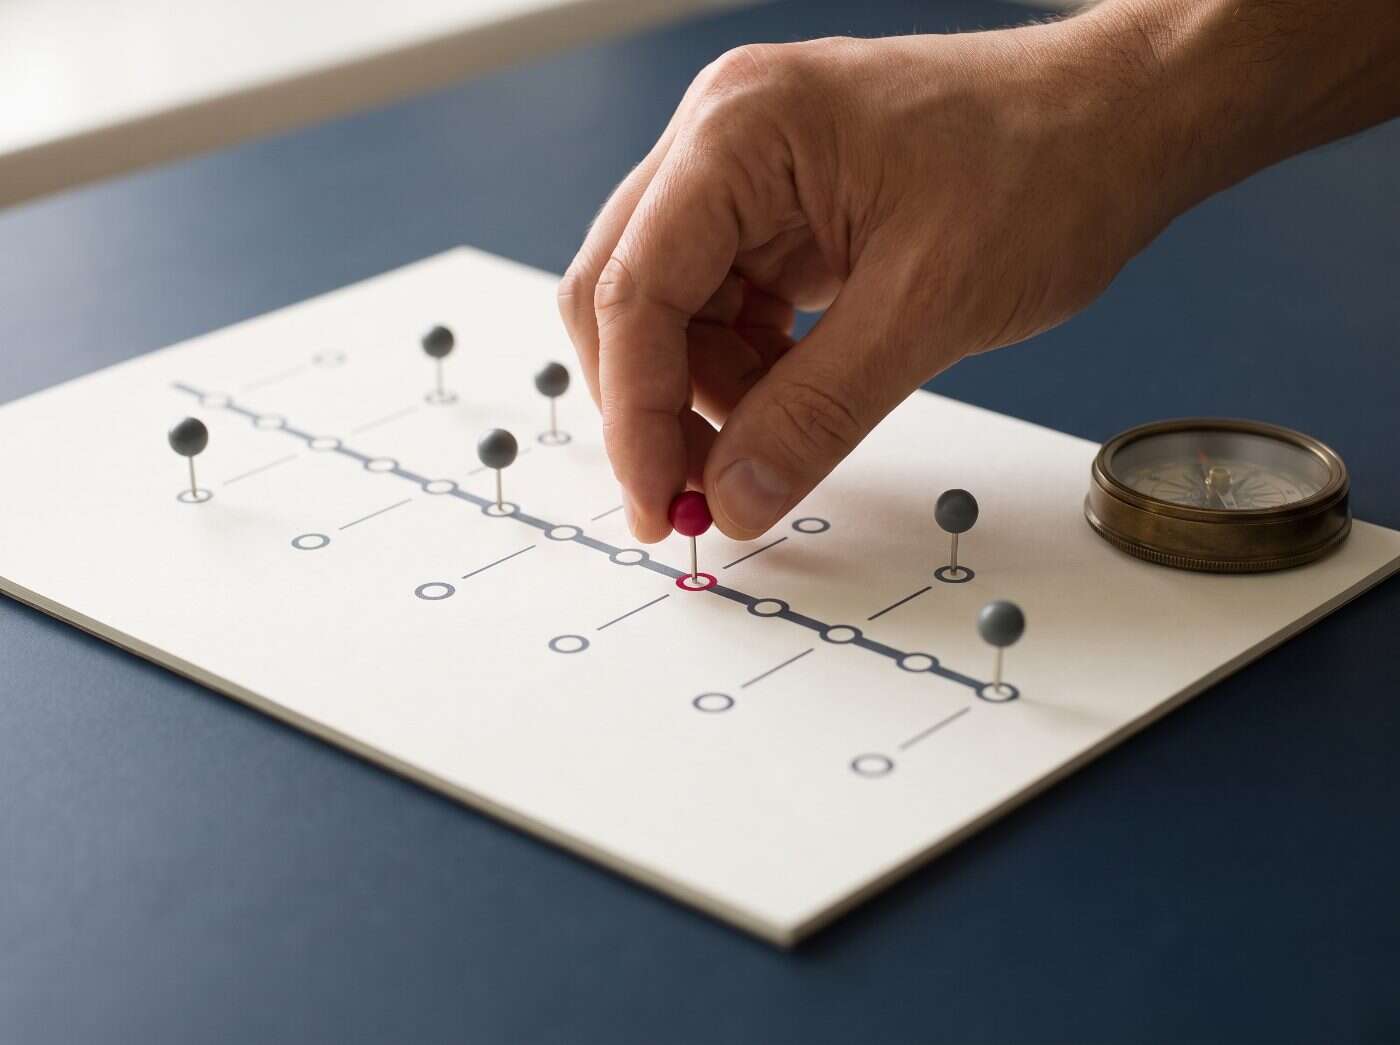
Hand placing a crimson pin on a printed twelve-step ISO 27001 roadmap laid on a navy desk
Phase 4 · control rollout
93
Annex A controls · 2022
22
Core policies · bilingual
12mo
Typical path to cert
100%
First-attempt Stage 2 pass
Annex A · ISO 27001:2022

Four control themes, ninety-three controls.

The 2022 revision consolidated 114 controls into 93 across four themes. We map each to an owner, a cadence, and a specific piece of evidence — not a paragraph of prose.

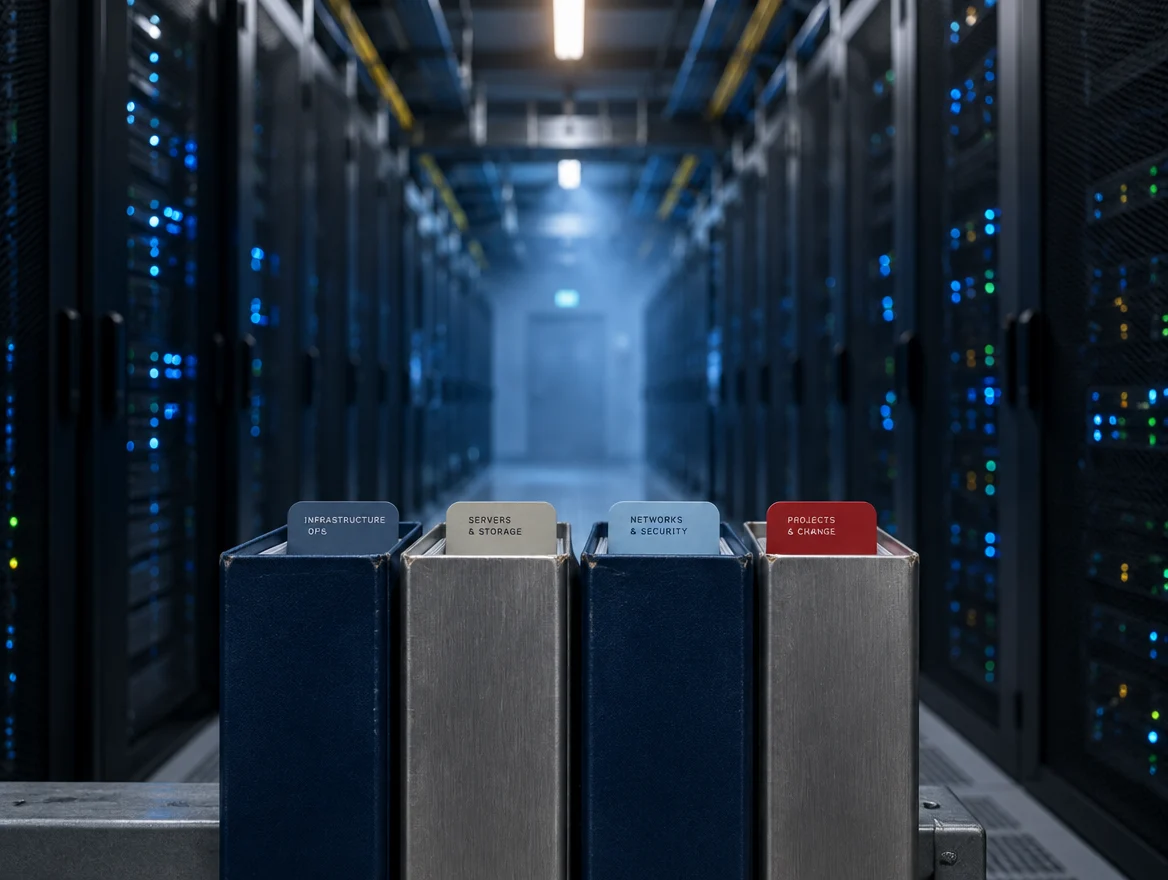
Four navy and steel file folders with colour tabs in a server room hallway, representing the four Annex A control themes
4 themes · 93 controls
A.5 · Organizational

Organizational controls

Policy, roles, supplier relationships, threat intelligence, information classification.

37 controls
A.6 · People

People controls

Screening, terms of employment, awareness training, disciplinary process, remote work.

8 controls
A.7 · Physical

Physical controls

Perimeters, entry, equipment, clear-desk, secure disposal, cabling and utilities.

14 controls
A.8 · Technological

Technological controls

Access, crypto, logging, vulnerability mgmt, secure dev, backups, network security.

34 controls
Why Noordev

We’ve shipped the thing, not just diagrammed it.

Our security practice sits next to the team that ships websites and runs Odoo implementations. Our policies account for how your company actually builds and operates — not how a checklist imagines it.
Two engineers at a standing desk reviewing a printed network diagram in a navy-walled Montreal office
Operators first
01 / Practitioners

Operators first, auditors second

Every lead is a practicing engineer, SRE, or sysadmin before they became a GRC consultant. Your controls will hold up to an auditor because they hold up to reality.

02 / Bilingual

EN, FR, and Arabic — natively

Policies and training materials delivered in the language your team speaks. Critical for Québec (Law 25), Morocco, and multinational teams with regulated LOBs.

03 / Scoped

Your ISMS, not ours

We don’t drop a 400-page template. We write a scope that matches your business, your risk appetite, and your audit pressure — and nothing more.

04 / Cross-framework

ISO 27001 · SOC 2 · Law 25 · PCI

Most clients need one framework loud and two frameworks quiet. We map once and satisfy all of them — without writing three sets of policies.

05 / Beyond cert

Year-one support built in

Certification is a milestone, not a finish line. Our engagements include the first year of surveillance prep, quarterly risk reviews, and incident support.
Client · Meridian Bank · Toronto
Noordev delivered our ISO 27001 certification in eleven months — and, more impressively, wrote policies our engineers actually read.
SR
Samira RahimiHead of Information Security, Meridian Bank
11mo
Assessment → Stage 2 pass
0
Major nonconformities
3×
Faster vendor questionnaire turnaround
$2.1M
Enterprise deals unblocked
Common questions

Before you book.

How long does ISO 27001 certification really take?

+

Twelve months is typical for a team of 20–200 starting from scratch. Smaller or better-organized teams can do it in 8–9. We publish a week-by-week plan before we start billing.

Can we do ISO 27001 and SOC 2 Type II in parallel?

+

Yes, and we usually recommend it. About 85% of the work overlaps. We write one policy set, one control matrix, and one evidence workflow — then satisfy both audits from the same system.

Do you bring a GRC tool or use ours?

+

Either. We’re tool-agnostic: Vanta, Drata, Tugboat Logic, Sprinto, or a well-configured Odoo for clients who prefer to keep everything in one system. We’ll recommend based on scale and budget.

What does the engagement cost?

+

Gap assessments start at $12,000 CAD. Full ISO 27001 implementations range $85k–$180k depending on scope, team size, and whether a vCISO is included. We send a fixed-fee proposal after the assessment.

Do you handle Québec Law 25 compliance?

+

Yes. Law 25 is bundled into our ISMS work for Québec clients at no extra cost — the policies, DPIAs, breach-response procedures, and consent flows map directly onto ISO 27001 Annex A.

Can you be our certification body?

+

No — by design. A certification body cannot also be your implementation partner. We prepare you and recommend three accredited CBs (Schellman, BSI, ISO-based in Canada) that have worked well for our clients.

● Start where you are

Book a 45-minute gap conversation. No sales pitch.

Tell us what you’re trying to achieve — a customer requirement, a board directive, a breach response — and we’ll tell you, honestly, what the next three months should look like.

This site is registered on wpml.org as a development site. Switch to a production site key to remove this banner.